Back to Projects
CYBERSECURITY LAB
Enterprise Identity Defense Lab
Built and hardened a Windows domain with Group Policy, user management, and security controls.
Lab Write-ups
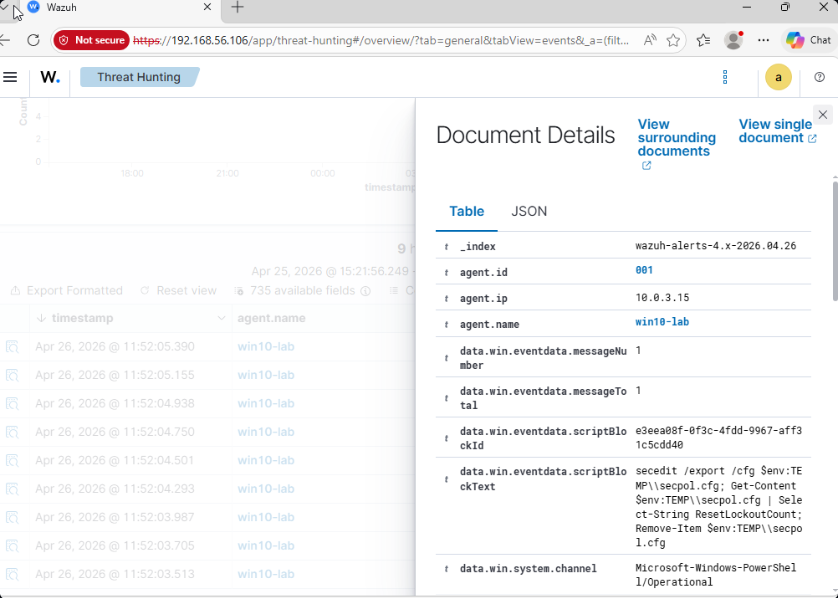
Kerberoasting Detection Lab
Traced a Kerberos service ticket request across the endpoint, domain controller, and Wazuh SIEM using Event IDs 4769, 4104, and 4688.
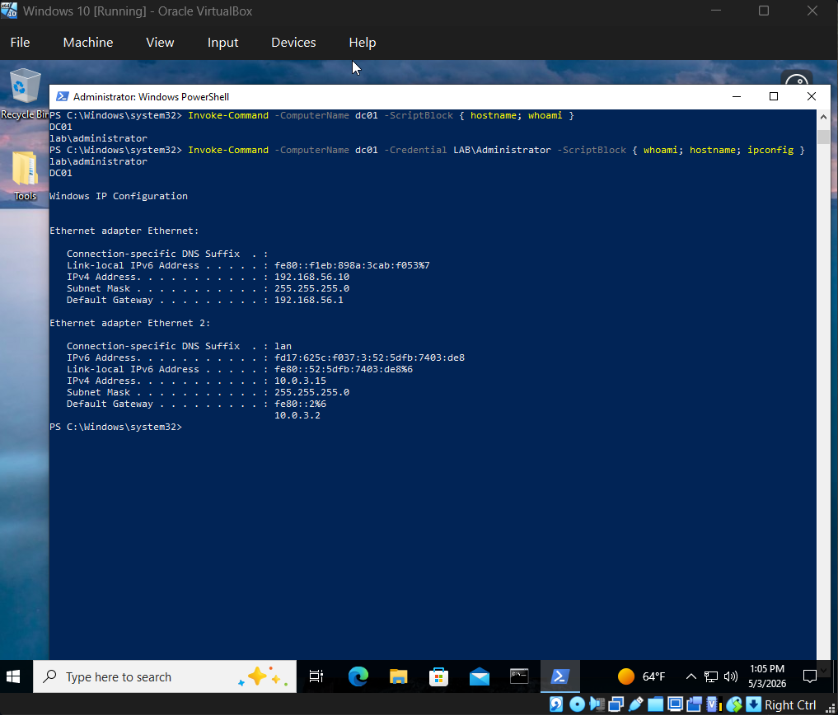
PowerShell Remoting Detection Lab
Simulated PowerShell Remoting from a workstation to the domain controller, then traced it through Event ID 4104 in Event Viewer and Wazuh.